// cat case-file.md
BaitWay
SOC PLATFORM · v1.0.1
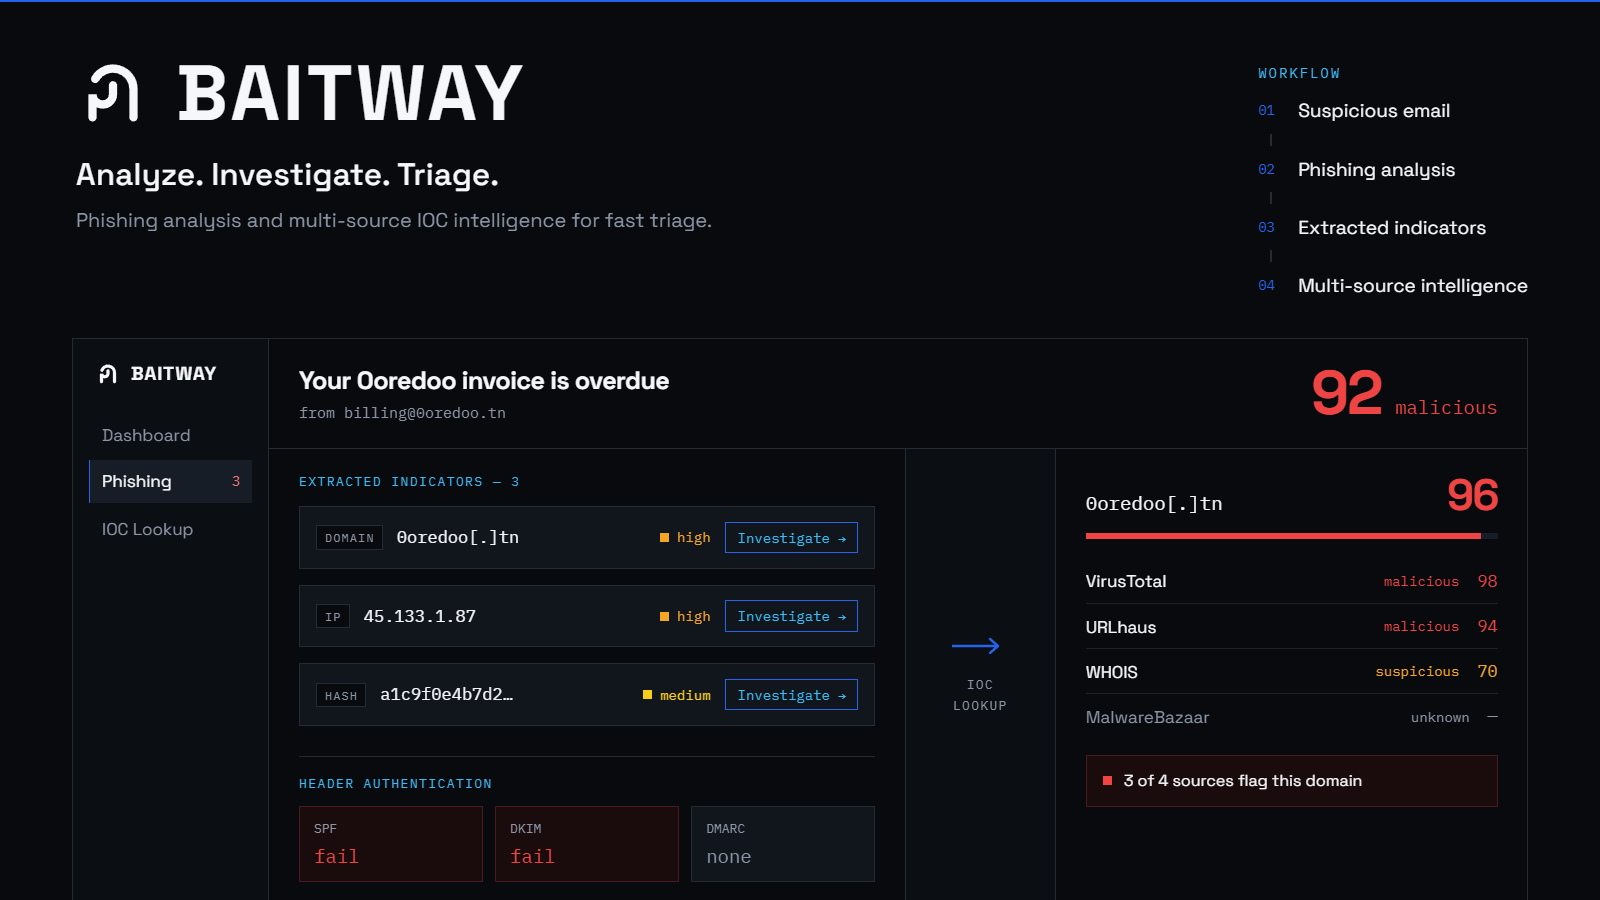
A SOC analyst platform that unifies the two most repetitive triage tasks — analysing suspicious emails and checking indicators of compromise — into one interface. Submit an email or an indicator, get an instant risk score and verdict enriched from multiple threat-intelligence sources. The first complete release shipped both modules integrated, and every phishing score is explainable down to the signal that produced it.
role: Phishing Portal (Module A)
team: with Iheb Ben Massaoud (2)
context: Internship · VadaSoft, Monastir
status: v1.0.1 · Sep 2026 · MIT
github.com/Givemeboga/Baitway ↗
release notes ↗
2
core SOC modules
5
threat-intel sources
0–100
risk score + verdict
55
automated tests in CI
// modules --soc
No single tool combined full-email analysis, an explainable score, a shared triage queue and a direct path to indicator lookup — that gap is BaitWay. Two engines behind one dashboard, both returning the same verdict scale, so an analyst reads phishing submissions and indicator lookups the same way.
🎣 Module A — Phishing Portal
MINE
Headers — SPF/DKIM/DMARC, Reply-To & display-name spoofing, origin IP
URLs — defanging, typosquatting (homoglyphs + edit distance), punycode, shorteners, raw-IP hosts
Attachments — MD5/SHA-256 hashed in memory (never executed), executables, macros, double extensions
Content — urgency, threats, credential & financial bait — French & English
Explainable scoring — weighted signals with diminishing returns; every point traces to a named reason
🔍 Module B — IOC Lookup
TEAMMATE
Server-side detection — IP / domain / URL / hash
Multi-source — VirusTotal, AbuseIPDB, URLhaus, MalwareBazaar, WHOIS/RDAP
Aggregation — many sources into one verdict
60-min cache — protects free-tier API quotas
History + export — search log, CSV / blocklist export
THE PHISHING → IOC BRIDGE
Any indicator extracted from an analysed email opens an IOC lookup pre-filled, with a link back to the originating submission — so the two modules collapse into one continuous workflow instead of copy-pasting between tools. It's the platform's core value, and the headline of v1.0.0.
SHARED FOUNDATION
JWT auth
Analyst / admin roles
Unified dashboard
OpenAPI docs
PostgreSQL + Alembic
Dockerized DB
CI · 55 tests
// triage --verdict
Every email and every indicator resolves to a single 0–100 score on one shared scale — so triage decisions stay consistent across both modules.
🟢 clean · 0–30
No sign of malicious activity
🟠 suspicious · 31–70
Questionable indicators — needs analyst review
🔴 malicious · 71–100
Confirmed malicious
// stack --list
BACKEND
Python 3.11+
FastAPI
SQLAlchemy
Alembic
JWT · bcrypt
FRONTEND
React 18
Vite
React Router
Axios
DATA & INFRA
PostgreSQL 16
Docker Compose
THREAT INTELLIGENCE
VirusTotal
AbuseIPDB
URLhaus
MalwareBazaar
WHOIS
// roadmap --phases
Phases 0–3 shipped in v1.0.0.
[x]
Phase 0 — Shared foundation · JWT auth, database, app shell, API contract
[x]
Phase 1 — Engines · phishing & IOC analysis built in parallel
[x]
Phase 2 — Interfaces · module UIs
[x]
Phase 3 — Integration · unified dashboard, phishing → IOC bridge, 55 tests in CI
[ ]
Phase 4 — Bonus · ML scoring, advanced export, PDF reports